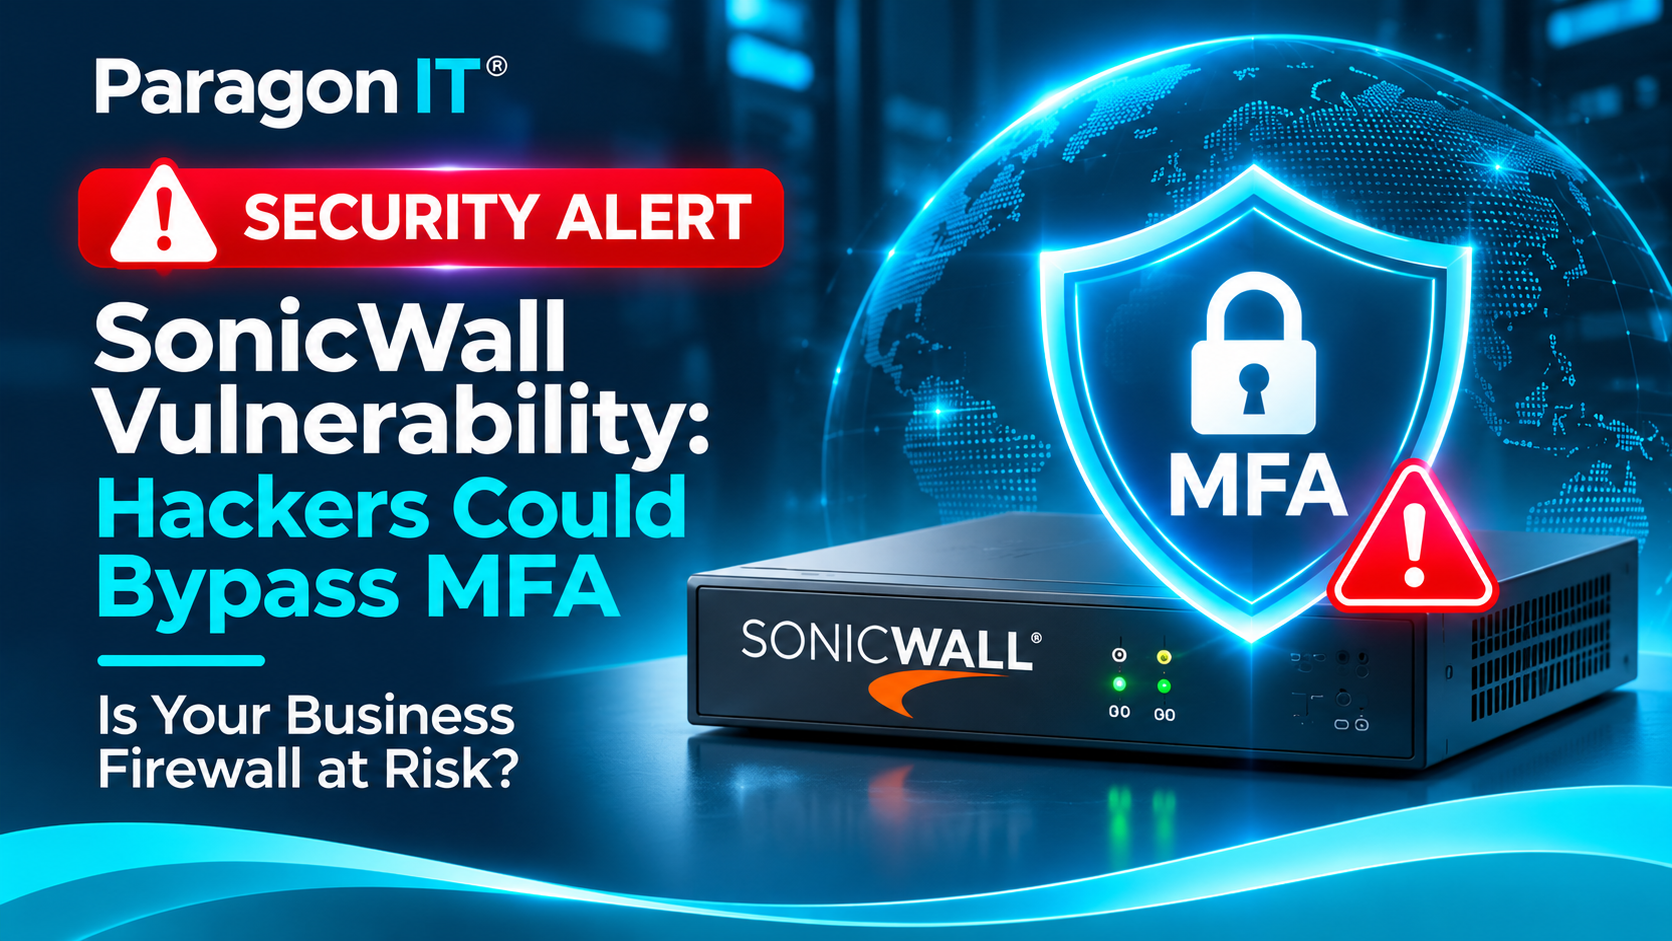
SonicWall Security Alert: Hackers Could Bypass MFA — Is Your Business Firewall at Risk?
A newly disclosed SonicWall vulnerability highlights why businesses must regularly review their firewall security, remote access and cybersecurity protection.
Your firewall is supposed to protect your business from unauthorised access. But what happens when attackers find a way around the authentication controls designed to keep them out?
On 6 November 2026, SonicWall disclosed a high-severity vulnerability, CVE-2026-19868, affecting certain SonicOS SSL VPN configurations.
The vulnerability could allow someone with valid credentials for an alternative authentication method to bypass SAML authentication controls, potentially including multi-factor authentication (MFA).
The issue has been added to the US Cybersecurity and Infrastructure Security Agency’s (CISA) Known Exploited Vulnerabilities catalogue.
For Australian businesses relying on SonicWall firewalls and remote VPN access, this is an important reminder: having MFA enabled does not automatically mean every authentication pathway is secure.
What Is the SonicWall MFA Bypass Vulnerability?
CVE-2026-19868 is an authentication enforcement vulnerability affecting SonicOS SSL VPN services when SAML authentication is enabled.
Under specific conditions, someone who already possesses valid credentials for an alternative authentication method could bypass the expected SAML login process and its associated MFA protections.
The vulnerability has a CVSS severity score of 7.1, classified as High by SonicWall.
Importantly, this does not mean every SonicWall firewall is vulnerable, or that attackers can exploit the flaw without credentials.
However, organisations running affected firmware and SAML-enabled SSL VPN services should treat the issue as a priority.
Why Should Australian Businesses Be Concerned?
Many businesses depend on firewalls and VPN connections to provide secure access to internal networks, cloud-connected systems and sensitive business information.
If authentication protections are bypassed, the potential consequences include:
- Unauthorised network access: Attackers may gain access through an affected remote-access connection.
- Exposure of sensitive information: Business data and internal resources could be put at risk.
- Compromised remote access: Employees and administrators may rely on VPN infrastructure with weakened authentication controls.
- Operational disruption: Investigating and containing a suspected intrusion can affect productivity and business continuity.
For small and mid-sized Australian businesses, a single overlooked vulnerability can create significant security exposure.
The key lesson? A firewall alone is not a complete cybersecurity strategy.
Which SonicWall Devices Are Affected?
The vulnerability affects certain SonicWall Gen7 and Gen8 devices running vulnerable SonicOS firmware when SAML authentication is enabled for SSL VPN access.
SonicWall has published security updates to address the issue.
Businesses should check their device model, firmware version and authentication configuration against the official SonicWall security advisory.
Do not assume your environment is protected simply because MFA is enabled.
What Should Your Business Do Now?
If your organisation uses SonicWall firewalls, the following actions should be prioritised.
1. Identify Your SonicWall Devices
Review your firewall inventory and determine which devices and SonicOS versions are deployed.
2. Check Your SSL VPN Authentication
Confirm whether SAML authentication is enabled and whether your configuration is affected by CVE-2026-19868.
3. Apply the Recommended Security Updates
Follow SonicWall’s official advisory and install the appropriate patched firmware as soon as practical.
4. Review VPN and Login Activity
Examine remote-access logs for suspicious connections, unusual login locations or unexpected authentication behaviour.
5. Strengthen Your Overall Security
Review access permissions, endpoint protection, patch management, security monitoring and incident response readiness.
Cybersecurity should be proactive, not something businesses address only after an incident.
How Paragon IT® Can Help Protect Your Business
At Paragon IT®, we help Australian businesses strengthen cybersecurity, manage IT infrastructure and reduce technology risks through practical, ongoing support.
Our services include:
🛡️ Firewall & Network Security
Review firewall configurations, remote access controls and potential security weaknesses.
🔐 Vulnerability Assessment & Patch Management
Identify vulnerable systems, prioritise security updates and support remediation.
🤖 AI-Assisted Threat Detection
Improve visibility into suspicious activity and emerging cybersecurity threats.
💻 Managed IT Services
Keep business systems maintained, monitored and supported with an accountable IT team.
🛡️ ParaGuardian SOC Protection
Strengthen your cybersecurity with 24/7 security monitoring, AI-assisted threat detection and expert incident response.
Our goal is simple: help businesses stay secure, reduce unnecessary IT complexity and respond to threats before they become bigger problems.
Don’t Wait for a Security Incident to Expose Your Weaknesses
The SonicWall MFA bypass vulnerability demonstrates an important cybersecurity reality:
Even trusted security technologies require regular updates, monitoring and independent verification.
For businesses relying on remote access and cloud-connected systems, keeping security controls current is essential.
Whether you need assistance reviewing your SonicWall environment, strengthening firewall protection or improving your overall cybersecurity strategy, Paragon IT® can help.
🛡️ Is Your Business Firewall Properly Protected?
Book a FREE Consultation with Paragon IT®
Speak with our specialists to review potential security risks and explore how our managed cybersecurity services can help protect your business.
Security References
- SonicWall Official Security Advisory: https://psirt.global.sonicwall.com/vuln-detail/SNWLID-2026-0014
- NIST National Vulnerability Database: https://nvd.nist.gov/vuln/detail/CVE-2026-19868
- CISA Known Exploited Vulnerabilities Catalogue: https://www.cisa.gov/known-exploited-vulnerabilities-catalog
- NHS England Cyber Alert: https://digital.nhs.uk/cyber-alerts/2026/cc-4886
Published 16 November 2026. This article provides general cybersecurity awareness information. Organisations should consult SonicWall’s official advisory for affected products, firmware versions and remediation instructions.