Cybersecurity Penetration Testing
Identify real-world security weaknesses before attackers do
Penetration testing shows exactly how an attacker could exploit weaknesses across your environment. We deliver practical, risk-focused testing that uncovers vulnerabilities, validates your controls and prioritises remediation — simulating real attack techniques the way an adversary would.
What is penetration testing?
Penetration testing is a controlled security assessment designed to identify and exploit vulnerabilities in a safe, authorised manner. Unlike standard vulnerability scans, penetration testing combines technical analysis, manual validation and attack simulation to determine which weaknesses are genuinely exploitable.
This helps your organisation understand not only where vulnerabilities exist, but how serious they are, what systems may be impacted and what actions should be taken first.
At Paragon IT, our approach goes beyond automated scanning. We simulate realistic attack techniques — the result is a clear understanding of your exposure, the business impact of identified risks and a practical roadmap to strengthen your security posture.
Our penetration testing process
Every engagement follows a structured methodology designed to deliver reliable, actionable results with minimal disruption to your business operations.
Scoping and Planning
We define the test scope, target systems, objectives, exclusions and engagement rules to ensure the assessment is aligned to your environment and business needs.
Reconnaissance and Discovery
We gather technical information about the target environment, identify exposed assets and map possible attack paths before active testing begins.
Testing and Exploitation
We perform controlled testing to validate vulnerabilities, attempt exploitation where authorised and assess the extent of potential compromise.
Risk Analysis
We evaluate the real-world impact of identified weaknesses — including potential access gained, lateral movement opportunities and business implications.
Reporting and Recommendations
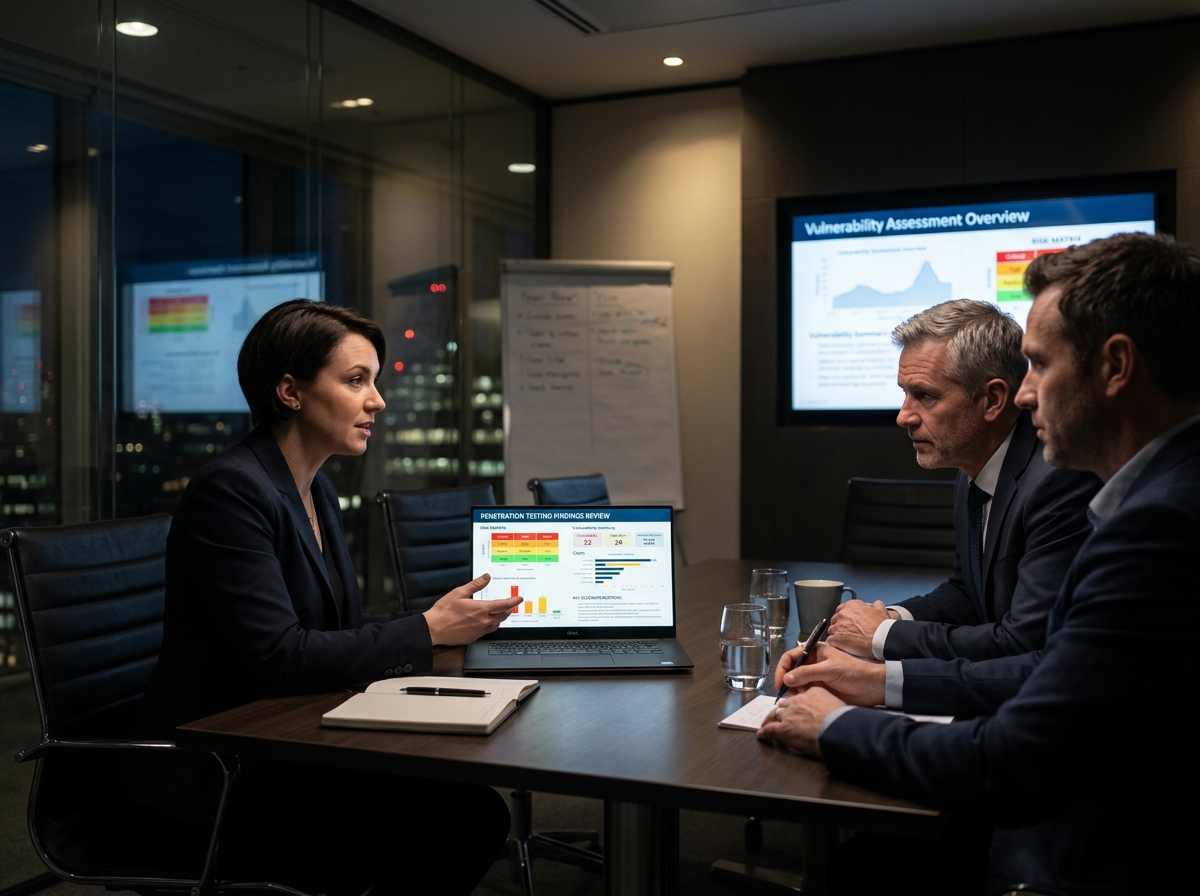
You receive a detailed report with executive summary, technical findings, risk ratings, evidence and prioritised remediation actions for both leadership and IT teams.
Remediation Support and Retesting
Where required, we work with your team to validate fixes and retest critical issues after remediation — confirming that vulnerabilities have been successfully addressed.
The benefits of penetration testing
Find Weaknesses First
Identify exploitable vulnerabilities before attackers do — replacing assumed security with validated, evidence-based confidence.
Validate Security Controls
Confirm that existing security investments — from firewalls to endpoint detection — are performing as expected in realistic attack scenarios.
Reduce Breach Risk
Reduce the risk of breach, downtime and data loss by addressing high-priority vulnerabilities before they can be exploited by real attackers.
Support Compliance & Governance
Provide evidence of security assessment and risk validation to support compliance, governance, audit requirements and cyber insurance obligations.
Prioritise Remediation
Focus security investment where it matters most — prioritised remediation based on real business impact, not theoretical severity scores.
Build Leadership Confidence
Give executives and boards evidence-based visibility over your security posture — moving from uncertainty to clear, documented understanding.
Frequently asked questions
What is the difference between vulnerability scanning and penetration testing?
How often should penetration testing be performed?
Will penetration testing disrupt our business operations?
Do you only test external systems?
Ready to talk?
Talk to a Paragon IT specialist today. Call 1800 877 565 or book a free consultation.