Cybersecurity Governance & Compliance
Build a stronger security posture with clear governance and compliance confidence
Cybersecurity is a business risk, a governance priority and core to operational resilience. We help you put the policies, frameworks, controls and oversight in place to reduce cyber risk and demonstrate due diligence — as a practical, actionable program.
What we deliver
Our Cybersecurity Governance & Compliance services are designed to help organisations create a structured and sustainable approach to security — aligning strategy with business goals, improving accountability and ensuring better preparedness for both cyber incidents and compliance reviews.
Cybersecurity governance frameworks
Policy and procedure development
Risk assessments and risk registers
Essential Eight alignment and uplift planning
Governance and compliance that work in the real world
Governance that supports real business outcomes
Effective cybersecurity governance gives your organisation the structure to make better decisions, assign responsibility, manage risk and improve accountability. Paragon IT helps you establish governance models that are realistic, scalable and aligned to your environment. We help define who owns what, what controls need to be in place, how risk should be measured and how leadership can maintain oversight without creating unnecessary complexity. This allows your business to move from reactive security decisions to a more strategic and managed approach.
Compliance without the confusion
Many businesses face growing pressure to meet cybersecurity expectations from customers, regulators, insurers and supply chain partners. But compliance can quickly become overwhelming without the right guidance. Paragon IT helps simplify the process. We assess your current state, identify gaps, prioritise actions and provide a roadmap to improve your posture over time. Rather than treating compliance as a checkbox exercise, we focus on building practical controls that improve both security and audit readiness.
Risk management with actionable visibility
A strong governance program starts with understanding your risks. We help businesses identify and assess cybersecurity risks across people, process, technology and third-party exposure.
Identify Key Cyber Risks
We assess your people, processes, technology and third-party relationships to surface the risks that matter most to your business.
Document Impact & Likelihood
Each identified risk is documented with its potential impact and likelihood — creating a clear, working risk register for the organisation.
Risk Treatment Planning
We develop treatment options — accept, mitigate, transfer or avoid — and help prioritise remediation actions based on business impact.
Control Mapping & Ownership
Security controls are mapped to specific risks with clear ownership assigned — making accountability visible and enforceable across the business.
Executive-Level Visibility
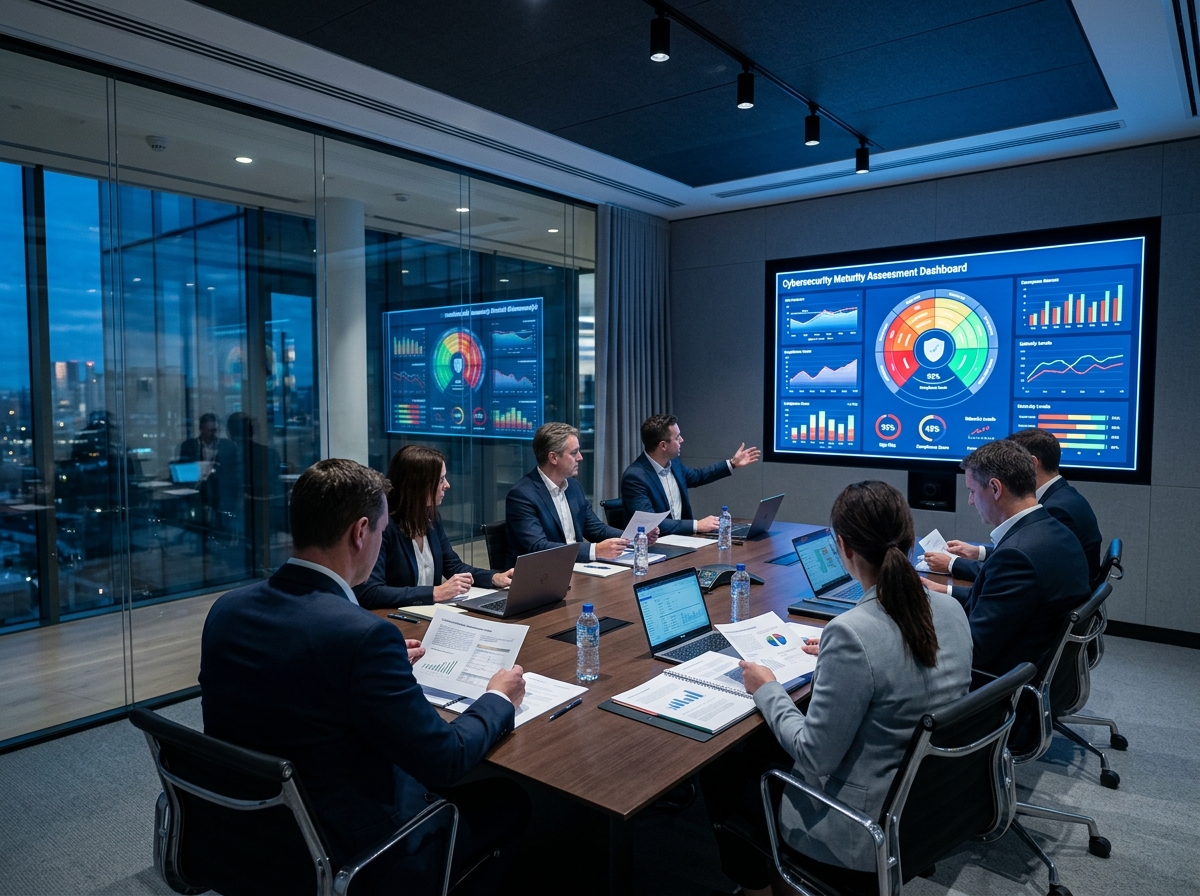
We translate security findings into clear reporting that gives leadership confidence the organisation’s security posture is understood and managed.
Better Investment Decisions
With clear risk visibility, leadership can make smarter decisions about where to invest in security improvements and which remediation actions to prioritise.
Frequently asked questions
What is cybersecurity governance?
Why is governance important for cybersecurity?
What is the difference between cybersecurity governance and compliance?
Can Paragon IT help with Essential Eight?
Ready to talk?
Talk to a Paragon IT specialist today. Call 1800 877 565 or book a free consultation.